Safe Autonomous Robot State Machine With Failsafes
Use this prompt to design a safe autonomous robot state machine with clear modes, failover logic, and practical safety checks.
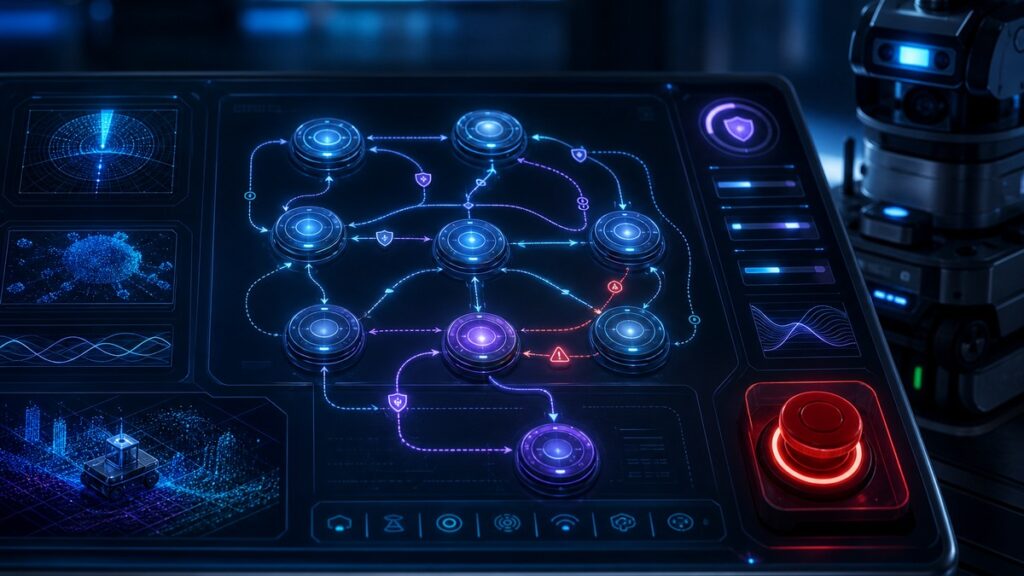
This prompt helps you design a safe autonomous robot state machine that is clear, testable, and built around failsafes instead of wishful thinking.
Use it to define robot modes, transition rules, recovery behavior, and shutdown logic before you implement control code or system docs.
Design a Safe Autonomous Robot Control State Machine
Build a structured control plan with explicit states, guarded transitions, recovery paths, and emergency fallbacks for autonomous operation.
COPY THIS PROMPT:
Act as a senior robotics systems engineer, safety-minded controls designer, and software architect.
Help me design an autonomous robot state machine with failsafes that is clear enough for implementation, review, and testing.
The robot may include sensors, navigation, motion control, docking, charging, task execution, error recovery, and emergency stop handling.
Your job is to produce:
– A concise purpose statement for the system
– A list of states with short descriptions
– Entry and exit conditions for each state
– Transition rules between states
– Sensor, timing, and health checks that gate transitions
– Recovery behavior for recoverable faults
– Safe fallback behavior for critical faults
– A manual override or emergency stop strategy
– Notes on logging, alerts, and watchdog handling
– A test checklist for validating the state machine
Design rules:
– Prioritize safety and predictable behavior over task completion.
– Keep states simple, named clearly, and easy to debug.
– Use guarded transitions instead of implicit behavior.
– Include timeouts for actions that may stall.
– Separate recoverable faults from critical faults.
– Include a fail-safe idle, hold, or shutdown state where appropriate.
– Avoid overly complex state nesting unless it adds real safety value.
– Do not invent hardware capabilities that were not provided.
– If important system details are missing, state the assumption clearly.
– Highlight any safety review questions that should be answered before deployment.
Output format:
1. System goal
2. Assumptions
3. State list
4. Transition table or bullet list
5. Failsafe logic
6. Fault handling rules
7. Example scenario walkthrough
8. Test checklist
9. Open safety questions
Robot details:
[Describe the robot type, sensors, actuators, environment, task, and any safety constraints]
Optional constraints:
[Add latency limits, battery rules, human proximity rules, docking needs, or recovery limits]
How to use this autonomous robot state machine prompt
What this prompt helps you do
A good autonomous robot state machine should make behavior easy to reason about under normal operation and under failure. This prompt pushes the AI to think in terms of explicit modes, safety checks, and controlled exits instead of vague automation.
- Define states with clear purpose and ownership
- Reduce ambiguous transitions and hidden behavior
- Separate recoverable errors from unsafe failures
- Build timeout and watchdog logic into the plan
- Support safer testing and code review
- Improve logging and debugging of edge cases
- Clarify when the robot should pause, hold, or stop
- Capture safety questions before implementation starts
💡 Pro Tip
Ask the AI to separate behavior into “normal operation,” “degraded operation,” and “safe stop” paths. That simple framing often produces a cleaner autonomous robot state machine because it forces the model to define what happens when sensors fail, tasks stall, or conditions become uncertain.
Example: From robot task to safer control flow
A warehouse robot patrols aisles, avoids obstacles, returns to dock when battery is low, and stops safely if sensors become unreliable.
Idle: Wait for mission start and confirm health checks.
Self_Check: Verify battery, comms, sensors, brakes, and
motion readiness.
Navigate: Move toward the assigned patrol point with
obstacle and localization checks.
Task_Execute: Perform the patrol or inspection action
only if all safety conditions remain valid.
Recoverable_Fault: Pause motion, retry a limited number
of times, and re-check sensor confidence.
Return_To_Dock: Trigger on low battery, mission end, or
repeated soft faults.
Safe_Stop: Stop motion, hold position, alert the operator,
and wait for manual intervention if the fault is critical.
Why this prompt works
Many AI requests for robotics control logic are too broad. If you simply ask for a control system, the result may skip the details that matter most: transition guards, fault classification, and the difference between retry and stop behavior.
This prompt asks for a full operating model. It makes the AI describe what each state does, what must be true before moving forward, and how the system should respond when something goes wrong.
It also encourages a safety review mindset. That matters because an autonomous robot state machine is only useful if the logic is understandable enough to test, audit, and maintain.
Frequently Asked Questions
Can I use this prompt for different robot types?
Yes. You can adapt it for mobile robots, inspection robots, delivery
robots, docking systems, or other autonomous platforms by changing the
robot details and safety constraints.
Will the AI output code or just a design?
It depends on how you frame the request. This version is designed to give
you a structured control plan, but you can ask for pseudocode or a code
skeleton if needed.
Should every fault trigger a full shutdown?
No. Some faults are recoverable, such as a brief sensor dropout or a
stalled action. Others are critical and should move the robot into a safe
stop state.
Can I use this prompt during testing?
Yes. It is useful before implementation, during design reviews, and when
building test cases for transitions, retries, and emergency behavior.
Should I trust the AI output without review?
No. Treat it as a planning aid. Review the logic with real system
constraints, safety requirements, and the people responsible for the
robot’s deployment.
When to use this prompt
Use this prompt when you need a safer structure for autonomous behavior, especially if the robot must handle changing conditions, low battery events, communication loss, or sensor uncertainty.
It is also useful when a project needs clearer documentation for how the robot should move from one mode to another without skipping essential safety checks.
If you are turning a concept into implementation, this prompt can help you define the autonomous robot state machine before you begin writing the real control logic.
Best practices for safer robot state design
Keep the number of states as small as practical. Too many tiny states can make debugging harder and can hide the real safety logic inside unnecessary complexity.
Use clear names that describe behavior, not just software structure. For example, names like Safe_Stop or Recoverable_Fault are easier to understand than vague labels that only developers recognize.
Always define what happens when timing, sensing, or communication becomes uncertain. A safe autonomous robot state machine should fail in a predictable way, not continue assuming everything is normal.
Finally, test the edge cases. Check what happens on startup failures, stuck transitions, repeated retries, low battery, and emergency stop activation so the real system behaves the way the design intends.
Summary
This prompt helps you create an autonomous robot state machine with explicit modes, guarded transitions, recovery rules, and clear failsafes.
Use it when you want a practical control design that supports safer implementation, better testing, and stronger review before deployment.
Looking for more practical AI prompts?
Explore AI Craft Pad for more useful prompts, tools and guides.
Browse Prompts →